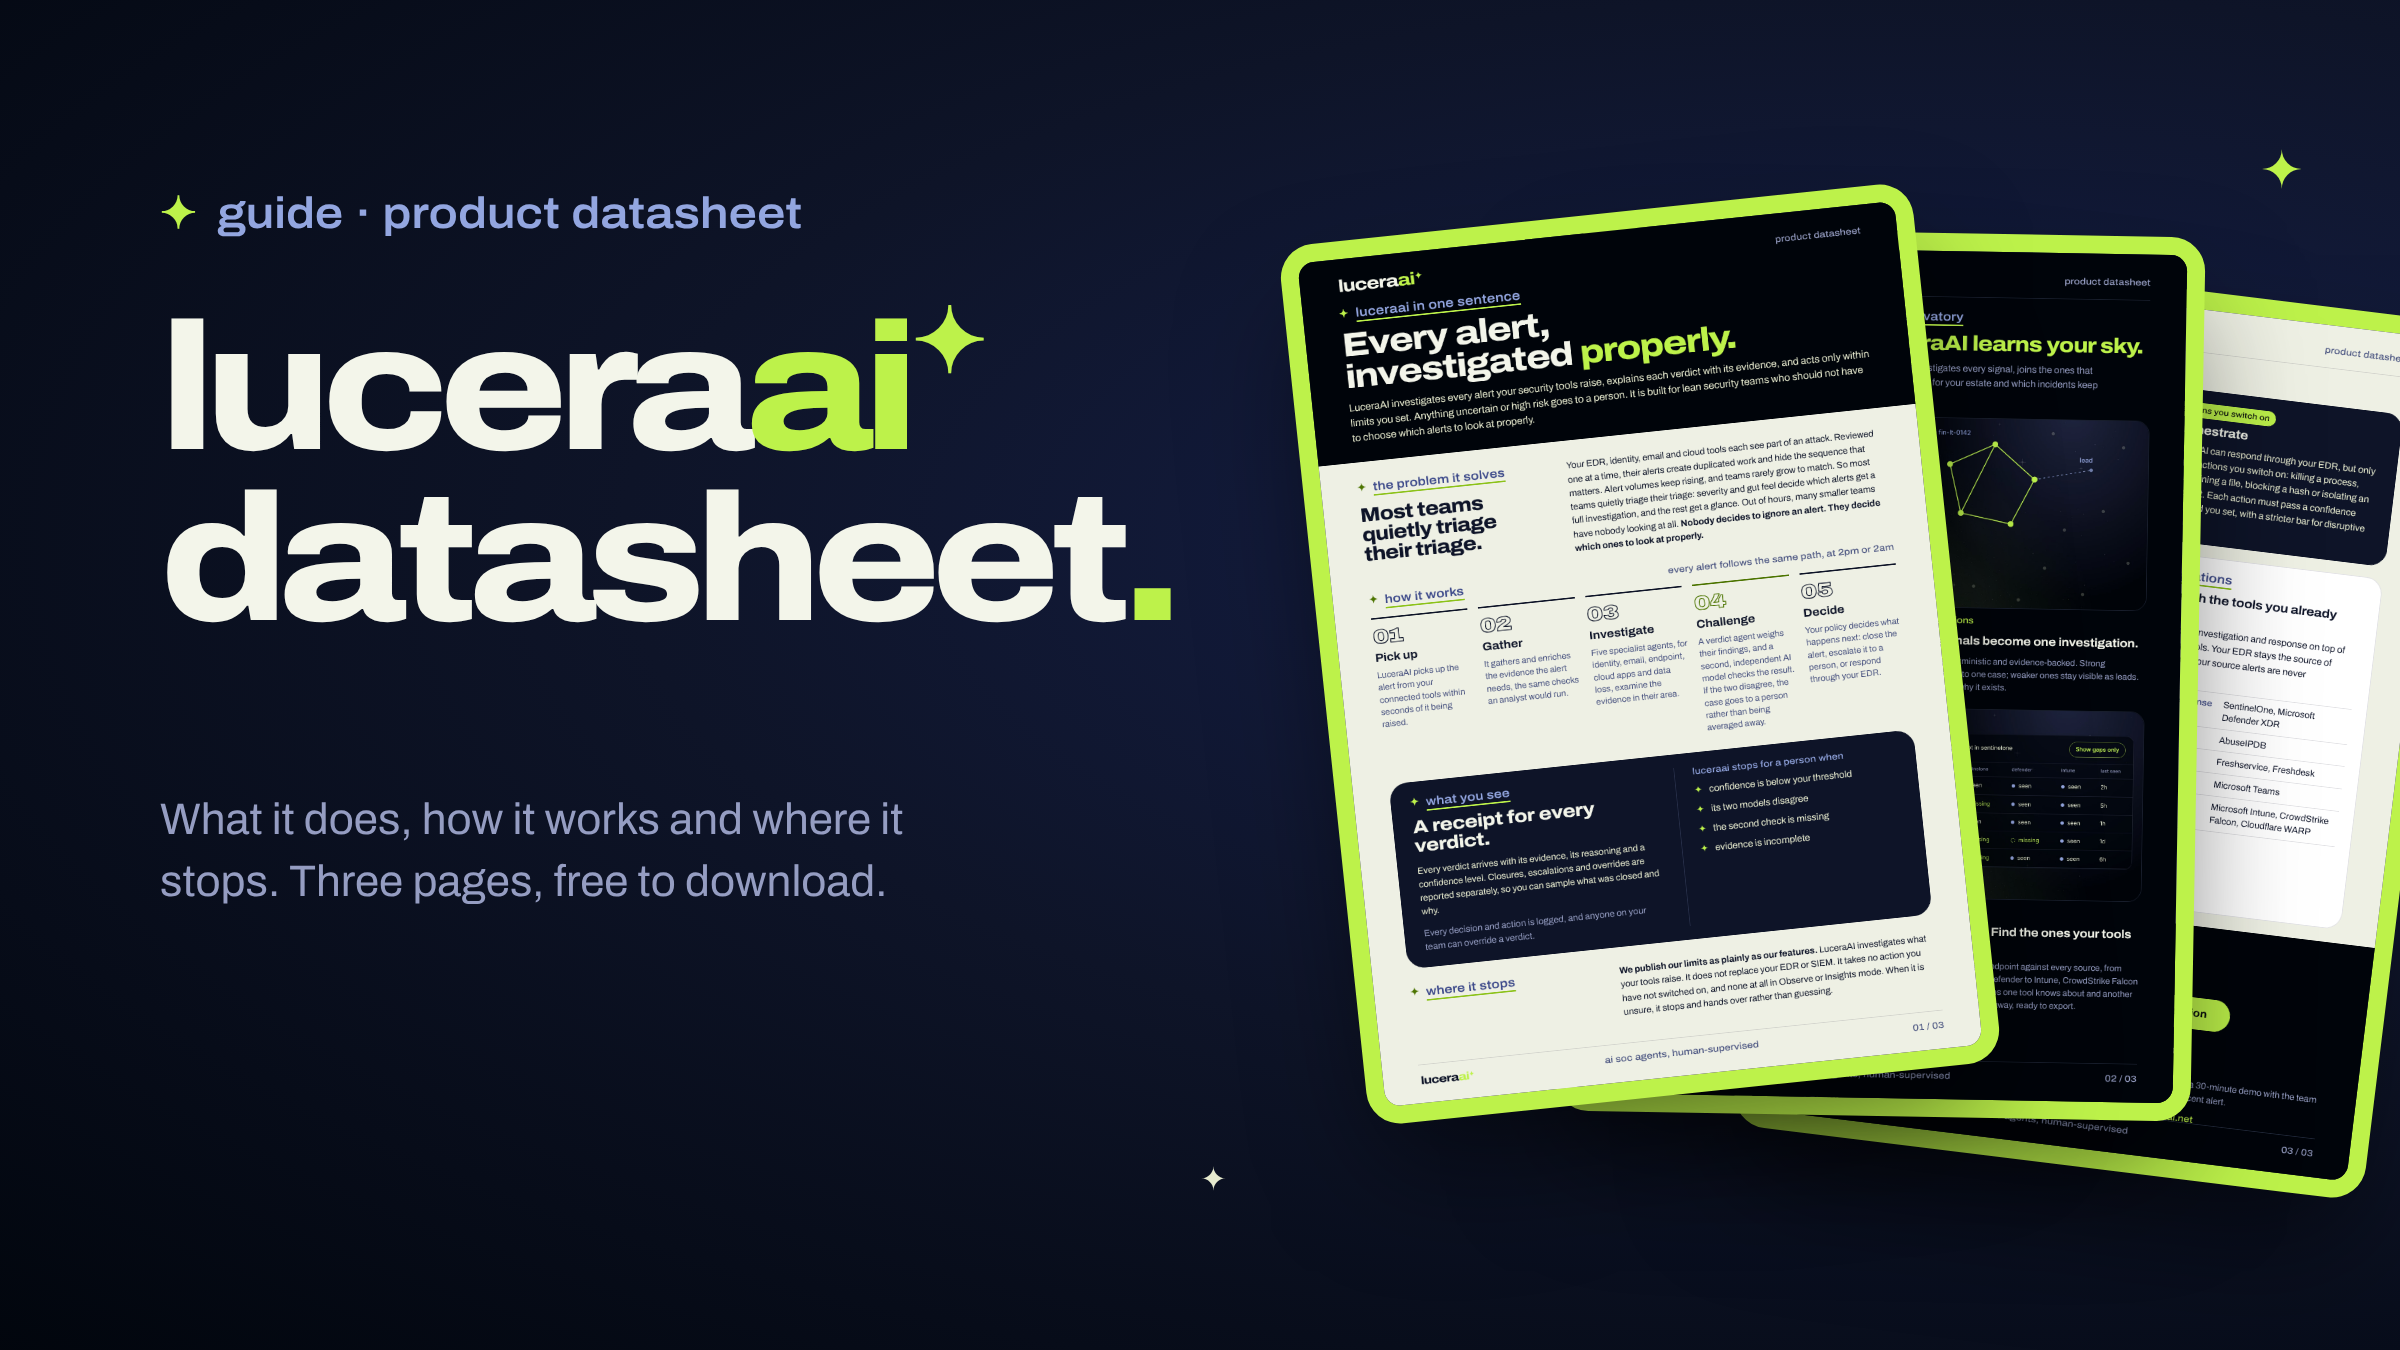
LuceraAI in one sentence
LuceraAI investigates every alert your security tools raise, explains each verdict with its evidence, and acts only within limits you set. Anything uncertain or high risk goes to a person.
It is built for lean security teams who should not have to choose which alerts to look at properly.
The problem it solves
Your EDR, identity, email and cloud tools each see part of an attack. Reviewed one at a time, their alerts create duplicated work and hide the sequence that matters.
Alert volumes keep rising, and teams rarely grow to match. So most teams quietly triage their triage: severity and gut feel decide which alerts get a full investigation, and the rest get a glance. Out of hours, many smaller teams have nobody looking at all.
Nobody decides to ignore an alert. They decide which ones to look at properly.
How it works
Every alert follows the same path, at 2pm or 2am.
- Pick up. LuceraAI picks up the alert from your connected tools within seconds of it being raised.
- Gather. It gathers and enriches the evidence the alert needs, the same checks an analyst would run.
- Investigate. A council of agents takes the case. Domain specialists for endpoint, identity, email, cloud apps and data loss each examine the evidence in their area, and a baseline comparator checks how similar alerts were decided before.
- Challenge. Two independent models from different providers must agree on the verdict, and a devil’s advocate argues it is wrong. If the models disagree, the case goes to a person rather than being averaged away.
- Decide. Your policy decides what happens next: close the alert, escalate it to a person, or respond through your EDR.
What you see: a receipt for every verdict
Every verdict arrives with its evidence, its reasoning and a confidence level. Closures, escalations and overrides are reported separately, so you can sample what was closed and why.
LuceraAI stops for a person when confidence is below your threshold, when its two models disagree, when the second check is missing or when evidence is incomplete. Every decision and action is logged, and anyone on your team can override a verdict.
Three operating modes, set per site
- Observe. LuceraAI investigates and reports. Nothing acts on your estate. This is where every evaluation starts.
- Insights. Verdicts and evidence flow into your existing tickets and notifications, still with no automated response.
- Orchestrate. LuceraAI can respond through your EDR, but only for the actions you switch on: killing a process, quarantining a file, blocking a hash or isolating an endpoint. Each action must pass a confidence threshold you set, with a stricter bar for disruptive actions.
Observatory: find the devices your tools miss
Observatory brings your endpoints from your security and device management tools into one inventory. Compare any two sources, for example Microsoft Intune and SentinelOne, and see which devices one tool knows about and the other has missed, such as laptops with no EDR agent.
Records only merge on exact identifiers. Hostname, IP address or user alone never merge two devices, and anything ambiguous goes to your team to decide.
Works with the tools you already own
LuceraAI adds investigation and response on top of your existing tools. Your EDR stays the source of detection, and your source alerts are never overwritten.
- Alerts and response: any EDR
- Enrichment: AbuseIPDB
- Tickets: Freshservice, Freshdesk
- Notifications: Microsoft Teams
- Asset sources: Microsoft Intune, CrowdStrike Falcon, Cloudflare WARP
People in the loop
LuceraAI does the evidence gathering and routine triage, so your analysts spend their time on decisions that need judgement. It is a colleague for your team, not a replacement for it.
Our own analysts can pick up escalations around the clock, so uncertain cases reach a person out of hours too. Every override your team makes is recorded, and an overturned pattern pauses automatically, so LuceraAI learns from your judgement.
Built in the UK
LuceraAI started inside a working MSSP, built by detection and response practitioners who still run it on live estates every day. We are a UK company, customer data is hosted in AWS London, and we work under UK law and UK GDPR. Your data is used to investigate your alerts and is not used to train AI models.
Where it stops
We publish our limits as plainly as our features.
- LuceraAI investigates what your tools raise.
- It does not replace your EDR or SIEM.
- It takes no action you have not switched on, and none at all in Observe or Insights mode.
- When it is unsure, it stops and hands over rather than guessing.
How to try it
Start with a two-week, read-only evaluation on your own alerts. Connect any EDR with read-only access, and LuceraAI runs in Observe mode. Nothing acts on your estate. At the end you receive an evidence pack with method notes, including a plain list of anything we could not measure.
Prefer to see it first? Book a 30-minute demo with the team who build it, and bring a recent alert.